Many of the core elements of a ransomware attack haven’t changed. Attackers still phish victims, exploit vulnerabilities, or purchase valid credentials to gain initial access to a network. From there, they may spread to other systems, escalate their privileges, and export data.
The New Extortion Economy: When Ransomware Doesn’t Need Encryption
Topics: Data Breaches, Incident Response, Data Exfiltration, Cyber Extortion
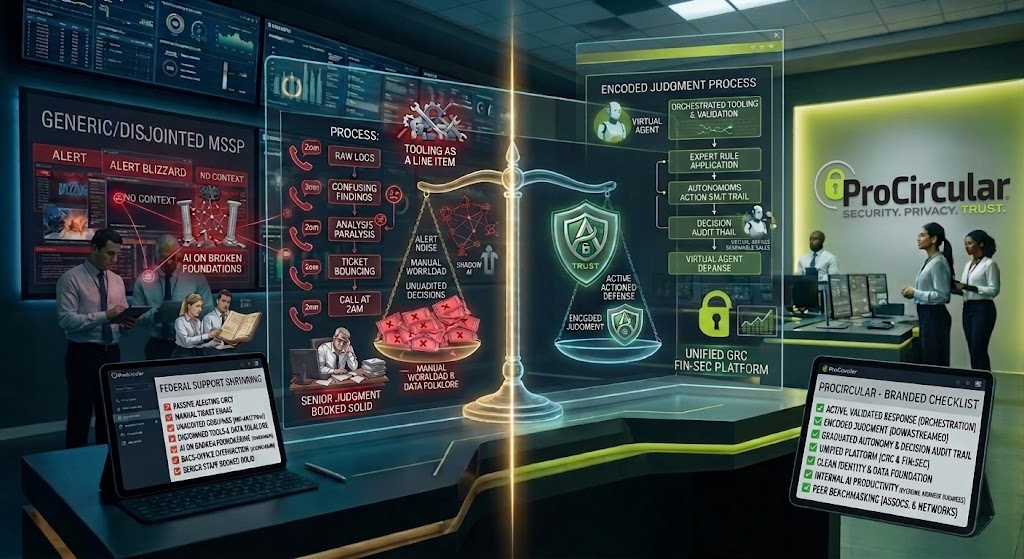
Before I was a lowly CEO, 22 of my 34 years in tech were spent as a customer of cybersecurity services, and the lack of capable MSSPs played a major role in my decision to start ProCircular. It's a topic near and dear to my heart: most cybersecurity firms or MSSPs leave clients wanting, and frequently, CISO teams end up training their cyber vendors. Incredibly frustrating.
Topics: Company News, cybersecurity, MSSP
AI-Native Security Starts With the Basics You Already Know
Fahmida Y. Rashid wrote a 20-year retrospective for Dark Reading (May 2026). If you sit on a board or approve security budgets, it's the clearest explanation I've seen in a long time of how we got here.
CMMC Phase 2 is Paused - The Homework is Still Due.
On July 13th, 2026, the DoW CIO released a statement mandating a pause in the Phase 2 rollout of the Cybersecurity Maturity Model Certification (CMMC) program, which was scheduled to go into effect on November 10th of 2026. Additionally, the article announced a 60-day review period of the program aimed at reducing red tape and barriers to entry for SMBs, along with a public Request for Information (RFI). Further public memos have been published outlining clarifications and implementation specifics for the statement, including outlines for interim actions for Department contractors and requirements for necessary contract revisions.
Topics: Government & Public Sector, Manufacturing, Compliance & Governance